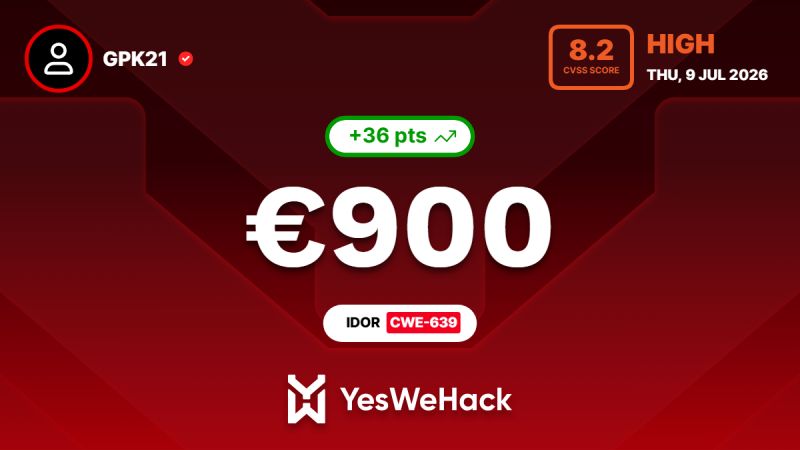
Unauthenticated IDOR in Notification API Enables Cross-User Read, Write, and Delete of Dashboard Notifications

An unauthenticated notification REST API exposed full CRUD operations over user dashboard notifications through POST, GET, and DELETE methods. Attackers could inject spoofed notifications into authenticated user dashboards, enumerate notifications by user identifier or sequential numeric ID, and delete arbitrary records without a session, token, API key, or ownership check.
Vulnerability: Insecure Direct Object Reference / Broken Object Level Authorization (CWE-639) · Severity: High — CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:H/A:N = 8.2; unauthenticated network access allowed low-confidentiality exposure of notification data and high-integrity modification/deletion of records, with no availability impact to the service.
Summary
A notification dashboard module exposed a REST controller, NotificationApiController.java, under:
/app/rest/notification-api/*